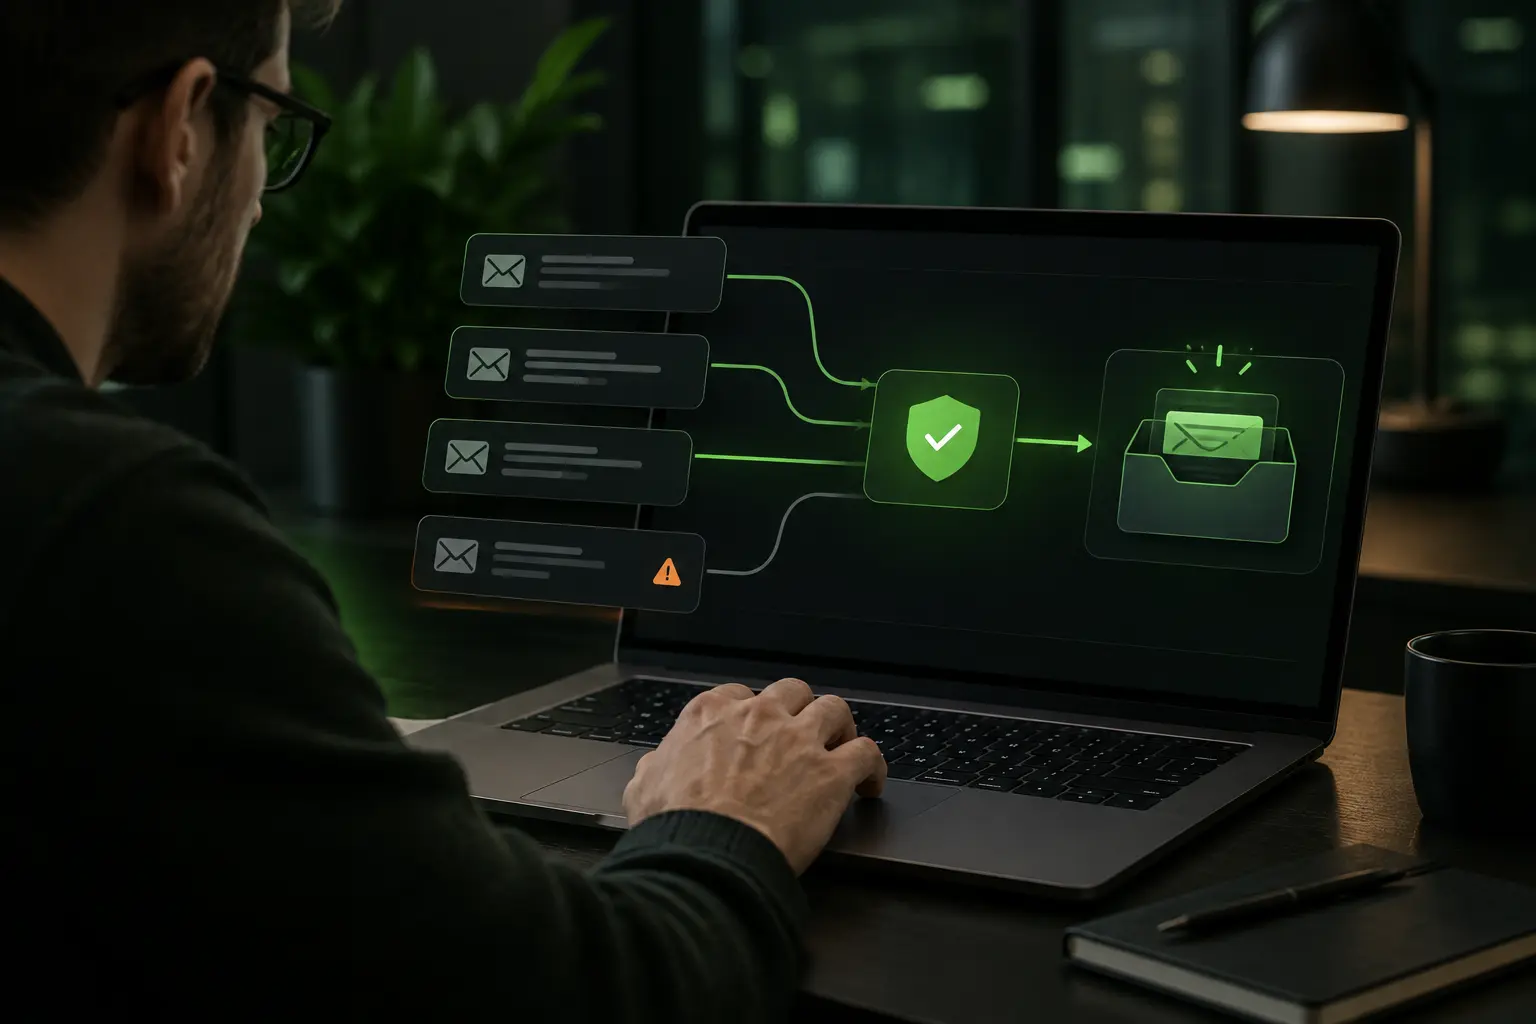

SPF, DKIM, and DMARC are the 3 email authentication protocols that verify your domain is authorized to send messages on your behalf. Since February 2024, Google and Yahoo require all 3 configured and aligned for any sender emitting more than 5,000 emails/day, under penalty of automatic rejection or mass spam classification. Unlike broader cold email best practices covering content, authentication concerns the technical layer of deliverability. A properly configured domain typically achieves 90-95% Gmail/Outlook inbox placement vs 55-70% without all 3 protocols. This article details each protocol, DNS records to create, recommended implementation sequence, verification tools, and 3 FAQ.
For a CTO, IT admin, growth marketer, or founder setting up deliverability for B2B cold email or transactional emails, this article covers complete technical configuration and validation.
On the agenda:
- What each protocol does (SPF, DKIM, DMARC)
- SPF configuration step by step (TXT record)
- DKIM configuration step by step (public/private keys)
- DMARC configuration in 3 phases (none / quarantine / reject)
- SPF and DKIM alignment with DMARC
- Free verification tools (MXToolbox, Mail-Tester, DMARC Analyzer)
- Classic mistakes and configuration pitfalls
- Impact of Google/Yahoo Sender Guidelines 2024
- 3 FAQ (propagation delay, multi-domain, volume requirements)
Key takeaways:
- SPF declares authorized servers to send via TXT record
- DKIM cryptographically signs each sent email
- DMARC tells mailboxes what to do if SPF/DKIM fails
- Alignment mandatory: the domain in SPF/DKIM must match the “From:”
- Since February 2024: Google and Yahoo require all 3 for > 5,000 emails/day
- Deliverability impact: 55-70% to 90-95% inbox placement
- Implementation sequence: SPF → DKIM → DMARC p=none → p=quarantine → p=reject, over 4-6 weeks
- Verification: MXToolbox SuperTool free + Mail-Tester full test
1. What each protocol does
SPF: send authorization
SPF (Sender Policy Framework) declares, via a DNS TXT record, the list of servers authorized to send on behalf of your domain. When a receiving server gets an email, it checks the sender domain’s SPF and verifies the sending IP is authorized.
Without SPF: the domain can be easily spoofed, and mailboxes penalize the deliverability score by 2-4 points.
DKIM: cryptographic signature
DKIM (DomainKeys Identified Mail) adds a cryptographic signature to each sent email’s header. The receiving server fetches the public key via DNS and verifies the signature. If valid = integrity guaranteed and sender authenticated.
Without DKIM: impossible to guarantee the content was not modified in transit, penalty 1-3 points.
DMARC: rejection policy
DMARC (Domain-based Message Authentication) is the upper layer: it tells mailboxes what to do if SPF or DKIM fails. Three possible policies: - p=none: observation only, no action - p=quarantine: spam folder for non-compliant - p=reject: total rejection of non-compliant
DMARC also produces daily reports sent to an email address specified in the record, allowing monitoring of impersonation attempts.
Combination of the 3
SPF checks send authorization. DKIM checks integrity. DMARC combines the 2 and applies a policy. All 3 must be configured AND aligned to be effective against spam and phishing.
2. SPF configuration step by step
Step 1: identify authorized servers
List all services that send emails on behalf of your domain: - Main email provider (Google Workspace, Microsoft 365) - Cold email / sequences tool (Lemlist, Instantly, Smartlead, Zeliq, Outreach) - Marketing automation (HubSpot, Mailchimp, Sendgrid) - Transactional tools (Sendgrid, Amazon SES, Postmark) - Eventual custom servers
Step 2: build the TXT record
Example for Google Workspace + Sendgrid + Outreach:
v=spf1 include:_spf.google.com include:sendgrid.net include:outreach.io ~allBreakdown: - v=spf1: SPF version 1 - include:: authorizes servers declared by the service - ~all: soft fail (recommended at start) - -all: hard fail (to activate after 30 days of stability)
Step 3: publish in DNS
Add this TXT record at the @ level (domain root) via your DNS manager (Cloudflare, Route 53, Google Domains, GoDaddy, etc.).
Watch limits: - Max 10 DNS lookups per SPF record (beyond, validation fails). Count each include: as 1-2 lookups. - Only 1 SPF record per domain (two records = failure).
Step 4: verify
Use MXToolbox SPF Check or dig TXT yourdomain.com command line. The record must appear with valid syntax.
3. DKIM configuration step by step
Step 1: generate key pair
Your sending provider (Google Workspace, Microsoft 365, Sendgrid, Zeliq) automatically generates a public + private key pair. The private key stays with the provider, the public goes in your DNS.
Step 2: publish public key in DNS
The provider gives you a TXT record to publish with a specific selector (often google._domainkey or s1._domainkey).
Google Workspace example: - Name: google._domainkey - Value: v=DKIM1; k=rsa; p=MIGfMA0GCSqGSIb3DQEBAQUAA4GNADCBiQKBgQ...
Step 3: activate DKIM at the provider
At Google Workspace: Admin console → Apps → Google Workspace → Gmail → Email authentication. Click « Generate new record » then « Start authentication » after publishing the DNS.
At Sendgrid, Zeliq, and others: similar activation button in deliverability settings.
Step 4: verify the signature
Send a test email to check-auth@verifier.port25.com or Mail-Tester. The report confirms if DKIM signature is valid.
Multi-selector for multi-provider
If you send via multiple providers (Gmail + Sendgrid), each provider has its own selector (google._domainkey, s1._domainkey, s2._domainkey). Publish all records, each email is signed by its sending provider.
4. DMARC configuration in 3 phases
Phase 1: p=none (observation, 2-4 weeks)
Create TXT record at _dmarc level:
v=DMARC1; p=none; rua=mailto:dmarc-reports@yourdomain.com; adkim=r; aspf=rp=none: no action, observation onlyrua=: email address receiving daily aggregate reportsadkim=r/aspf=r: relaxed alignment (recommended start)
For 2-4 weeks, analyze aggregate reports received. They list all servers sending on your domain and whether SPF/DKIM checks pass.
Phase 2: p=quarantine (2-4 weeks)
Once 95%+ of sends pass SPF or DKIM:
v=DMARC1; p=quarantine; rua=mailto:dmarc-reports@yourdomain.com; pct=25; adkim=r; aspf=rp=quarantine: spam folder for non-compliant messagespct=25: apply to 25% of non-compliant messages (gradual ramp)
Gradually increase pct=25 → pct=50 → pct=100 over 2-4 weeks.
Phase 3: p=reject
Final, strictest policy:
v=DMARC1; p=reject; rua=mailto:dmarc-reports@yourdomain.com; adkim=s; aspf=sp=reject: total rejection of non-compliantadkim=s/aspf=s: strict alignment (subdomain must match exactly)
At this stage, your domain is protected against spoofing and your legitimate emails are marked authenticated by mailboxes.
Watch progression errors
Moving directly to p=reject without observation phase risks blocking legitimate unidentified sends (e.g., a forgotten CRM tool). The none → quarantine → reject progression over 6-8 weeks is standard.
5. SPF and DKIM alignment with DMARC
The alignment principle
DMARC isn’t satisfied just that SPF or DKIM passes: it requires the authenticated domain matches the email’s « From: » domain.
Relaxed alignment (r): subdomains accepted. An email From: notifications@app.zeliq.com passes SPF alignment if SPF validates zeliq.com.
Strict alignment (s): exact subdomain required. Same email requires SPF to validate app.zeliq.com specifically.
Why alignment can fail
Typical case: your cold email tool sends from From: john@yourdomain.com but via the vendor infrastructure Return-Path: bounce@tool-vendor.com. SPF validates tool-vendor.com, not yourdomain.com = alignment failure.
Solution: ask the vendor to configure a « custom domain » or « aligned return-path » with your domain.
6. Free verification tools
MXToolbox SuperTool
mxtoolbox.com/SuperTool.aspx. Checks SPF, DKIM, DMARC in one click, with detailed diagnostics. Free unlimited.
Mail-Tester
mail-tester.com. Send a test email to the generated unique address, get a score out of 10 with 3-protocol verification.
DMARC Analyzer / Postmark DMARC
Specialized tools to analyze DMARC aggregate reports. Native XML format is unreadable; these tools transform it into interpretable dashboards. Freemium (free up to 5-10,000 messages/month).
Google Postmaster Tools
postmaster.google.com. Official Gmail view on your domain reputation + SPF/DKIM/DMARC compliance statistics. Free, configure if you send > 1,000 emails/day to Gmail.
7. Classic mistakes
Mistake 1: SPF record broken by addition
Each service addition (new CRM, transactional tool) adds an include: to SPF. Easy to exceed the 10 DNS lookups = silently broken SPF.
Solution: use an SPF Flattener tool (like DMARCLY, EasyDMARC) that compresses includes into flat records.
Mistake 2: DKIM not activated after DNS publication
Publishing the DNS record isn’t enough; you must also activate DKIM at the sending provider. Often-forgotten step = non-functional DKIM despite visible DNS record.
Mistake 3: direct DMARC p=reject jump
Without p=none then p=quarantine phase, risk of blocking 5-15% of unidentified legitimate sends. Always 6-8 weeks progression.
Mistake 4: forgetting cold outbound subdomain
Sending cold email from @yourdomain.com (main domain) risks degrading domain reputation if volume miscalibrated or accidental blacklist. Use a dedicated subdomain @outreach.yourdomain.com with proper DKIM/SPF/DMARC.
Mistake 5: no post-implementation monitoring
Once configured, let it run without monitoring = risk of silent drift (provider changing IPs, spam trap touched). Google Postmaster Tools + weekly DMARC reports prevent surprises.
Zeliq and integrated deliverability configuration
Zeliq combines a 450 million B2B contact database with waterfall enrichment, multichannel sequences, and integrated email verification that filters invalid addresses before send. A reduced bounce rate directly protects domain reputation and the validity of SPF/DKIM/DMARC configurations over time.
8. Impact of Google/Yahoo Sender Guidelines 2024
What changed since February 2024
Google and Yahoo now require volume senders (> 5,000 emails/day Gmail):
- SPF configured and aligned with From domain
- DKIM configured and signing each email
- DMARC configured minimum
p=nonewith rua address - Spam complaint rate < 0.3% (0.1% ideal)
- Functional one-click unsubscribe button in marketing emails
Consequences for B2B cold email
A B2B cold email typically doesn’t reach 5,000 sends/day per domain, but if you scale to 5-10 SDRs on the same domain, you quickly approach the threshold. Sender Guidelines compliance has become standard regardless of volume.
Compliance verification
Quick test: send an email to a personal Gmail address from your cold tool, open the message, click « Show original ». Look for mentions SPF: PASS, DKIM: PASS, DMARC: PASS. If any is missing, priority fix.
9. Frequently asked questions
How long does DNS propagation take after adding records?
5 minutes to 48 hours depending on TTL (Time To Live) configured on your DNS zone and the recipient’s ISP. DNS propagation isn’t instant: when you add a TXT record at your registrar (GoDaddy, Cloudflare, Route 53, Google Domains), the new record propagates progressively to global DNS servers. Factors influencing duration: (1) record TTL: shorter (300 sec = 5 min), faster propagation; long TTL (86400 sec = 24 h) slows. (2) Recipient DNS cache: some providers (Gmail, Outlook) cache SPF/DKIM/DMARC records 4-24 hours. (3) DNS provider: Cloudflare typically propagates in 1-5 minutes, GoDaddy in 15-60 minutes, Route 53 in 5-10 minutes. Practical recommendation: lower TTL to 300 sec 48 hours before planned modification, apply the change, wait 15 minutes, test with Mail-Tester. If the record appears correctly in MXToolbox, propagation is complete for public DNS servers. For recipient mailbox caches, count 4-24 hours for full rollout. Never leave a broken record more than 24 hours: mailboxes fall back on their old cache and cushion the error, but recurring change creates reputation instability.
Should SPF/DKIM/DMARC be configured for each subdomain?
Yes, each subdomain used to send emails needs its own SPF/DKIM/DMARC configuration (separate DNS retrieval), even if the main domain is already configured. The principle: DNS treats each subdomain as an independent zone. A TXT record at zeliq.com doesn’t automatically apply to app.zeliq.com or outreach.zeliq.com. Typical use case in B2B outbound: main domain @zeliq.com for corporate emails (HR, contracts, invoices); a dedicated @outreach.zeliq.com subdomain for cold email avoids contaminating main reputation if campaign spam-flagged. This dedicated subdomain must have: (1) own SPF declaring the cold tool used, (2) own DKIM with specific selector, (3) own DMARC. DMARC tip: configure a _dmarc.outreach.zeliq.com record with its own policy, independent of _dmarc.zeliq.com. This allows p=none on outbound subdomain during learning phase without exposing the main. Warning: a subdomain without DMARC inherits by default from parent domain DMARC. If parent is p=reject and you send from a misaligned subdomain, all emails are rejected. Always verify alignment before strict activation.
How to verify send volume to know if Sender Guidelines apply?
Google Postmaster Tools displays your detailed Gmail volume free and alerts when you approach the 5,000 emails/day threshold triggering enhanced requirements. Configuration: go to postmaster.google.com, add your domain, prove ownership via DNS TXT record (5-minute setup), wait 24-48 hours for data appearance. The dashboard displays: volume sent to Gmail per day, spam-reported rate, IP/domain reputation, SPF/DKIM/DMARC compliance. The 5,000 threshold applies to emails to gmail.com and googlemail.com only (not total across providers). If you send majority B2B to pro domains, Gmail traffic may be 30-50% of total volume; an outbound team of 3-5 SDRs at 100 emails/day each sends ~1,500-2,500 to Gmail, below threshold. For 10+ SDR team or multichannel, threshold reached. Recommendation: even below threshold, proactively configure SPF+DKIM+DMARC minimum p=none, because (1) Yahoo applies similar rule, (2) all mailbox providers penalize absence even below threshold, (3) you’re ready to scale without emergency reconfiguration. Postmaster Tools also alerts on deliverability issues (rising spam rate, blacklist), useful even for small teams.
10. Conclusion: 3 actions to run
Verify current configuration within 7 days via MXToolbox SuperTool. SPF, DKIM, and DMARC must all 3 appear with green status. If any is missing, priority fix before any volume cold send.
Configure DMARC in
p=nonewithin 15 days if absent. rua address to a dedicated report inbox. Weekly analysis for 4 weeks before ramping top=quarantine.Install Google Postmaster Tools within 30 days. 5-minute setup, data visible within 48 hours. Free monitoring of domain reputation essential in 2026.
Protect your deliverability upstream with integrated email verification
Zeliq combines 450 million B2B contacts, waterfall enrichment with integrated email verification, and multichannel sequences. Bounce rate reduced to 1-3%, domain reputation preserved. Account created in 2 minutes.
Try for freeAnd if you want your SPF/DKIM/DMARC configurations to remain effective over time thanks to upstream email verification, try Zeliq for free: sourcing, verification, and multichannel sequences in one interface, no credit card required.